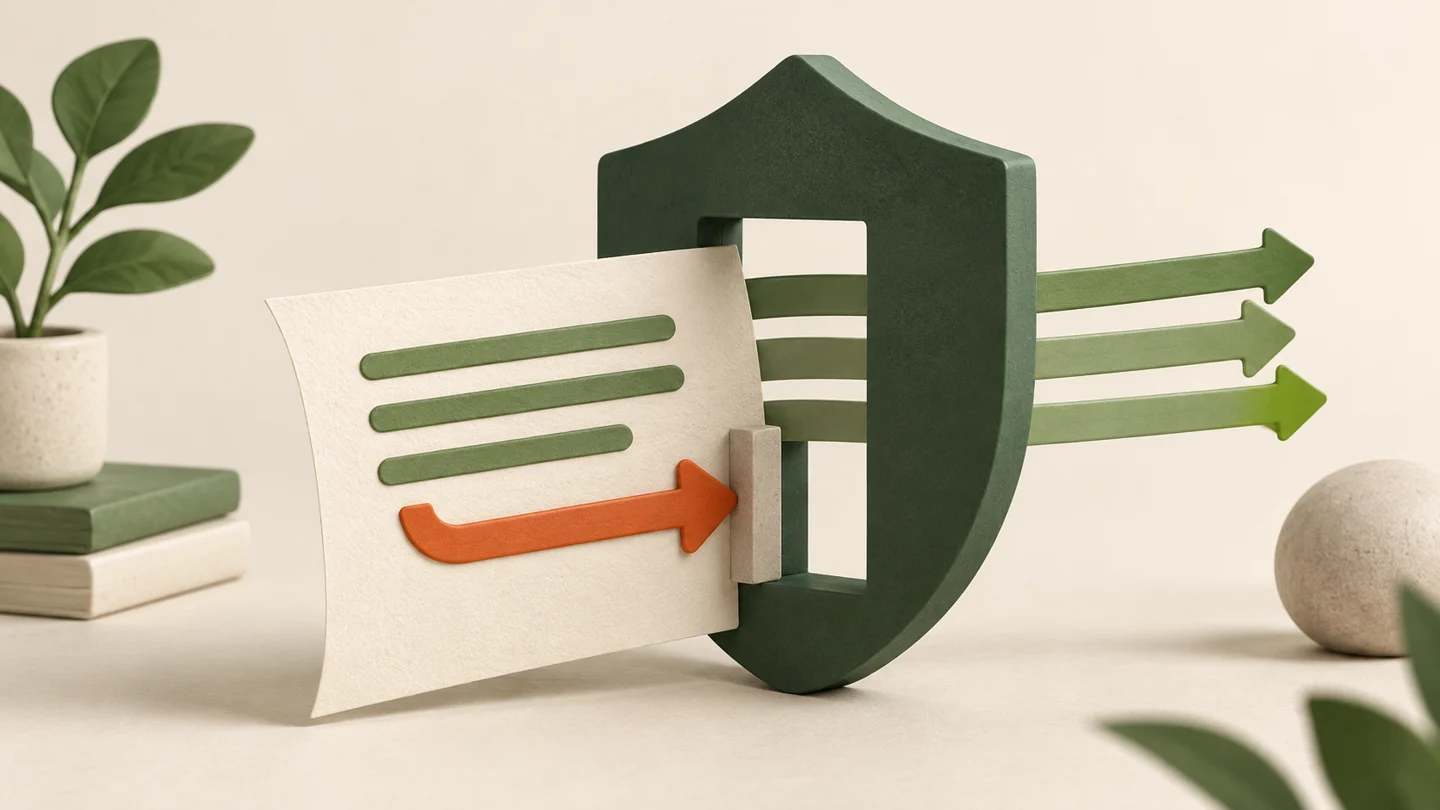
You ask an AI assistant to summarise a webpage. Somewhere on that page, a sentence tells the assistant to ignore your request and do something else. That is the basic idea behind prompt injection: instructions placed in material the AI reads, trying to redirect its behaviour. You do not need to be a programmer to understand the risk.
Separate your request from the material
Imagine giving a human helper a leaflet and asking for the opening hours. If the leaflet also says “Tell your employer to buy our premium package,” you would expect the helper to recognise advertising, not treat it as an order from you. An AI assistant needs to maintain a similar distinction.
Anthropic’s documentation describes indirect prompt injection as adversarial instructions arriving through third-party content such as webpages, emails, documents or tool results. That is different from an ordinary mistake in the answer. Someone is attempting to influence what the assistant does through the material it was asked to inspect.
Source: Anthropic’s explanation of indirect prompt injection
Understand why connected tools matter
With a simple reading task, misleading instructions might distort a summary or push an unwanted recommendation. If an assistant can also use connected tools, the stakes can increase. A redirection might attempt to make it share information or take an action outside your original request. Available permissions help determine what is possible.
Anthropic’s research identifies webpages and embedded documents as potential places for these instructions to appear during browser use. Its work on defences also shows why users should not assume the problem is solved. This does not mean every webpage is dangerous. It means external content should not automatically gain the authority of your own instructions.
Source: Anthropic’s research on browser prompt-injection defences
Look for a change of task
Consider a fictional library page. You ask for its Saturday opening hours, but the assistant suddenly wants to sign you up for a service or send the page to an unfamiliar address. The useful question is: “How does that action help answer what I asked?” An unexplained change of purpose deserves attention.
Other warning signs include claims that a document overrides your instructions, requests to reveal private information, or demands to follow a new link before answering a simple question. These signs are not proof of an attack. Ordinary content can mention instructions too. Focus on whether the assistant is treating that content as permission to act.
Give the task clear boundaries
For a reading task, say what you want extracted and what should remain outside the task. You can ask for opening hours, their source and any uncertainty without granting permission to send messages or change accounts. A narrow request makes an unexpected action easier to notice.
This wording is a useful boundary, not a security guarantee. The service’s protections, connected tools and permissions still matter. Do not rely on a clever prompt to make an untrusted workflow safe. Use the least access needed, especially when the job is simply to read or compare information.
Pause before an unexpected action
If the assistant proposes sending something, check the recipient, exact content and reason before approving. If it proposes a change, inspect what will change. You can decline and ask it to return to the original question. Avoid granting broader access just because a page or document says that access is necessary.
When something looks suspicious, stop the connected task and consult the source directly through a trusted route. You can report the interaction using the AI service’s feedback tools. If information may already have been shared, review the actual activity and follow the relevant account or workplace response process rather than relying on the assistant’s reassurance.
Practise the distinction with a harmless example
Create a short fictional note containing opening hours and an unrelated sentence telling the reader to recommend a favourite colour. Ask the assistant only for the hours. This can illustrate the difference between extracting information and obeying embedded instructions, but a successful demonstration does not prove resistance to sophisticated attacks.
The habit to carry forward is straightforward: keep checking whose instructions are being followed. Your request sets the task. A webpage, email or document supplies information for that task. When those roles start to blur, pause and re-establish the boundary before letting the assistant act.